 Purchase on AWS Marketplace
Current-state architecture
Documented system boundaries, representative agent workflows, integration touchpoints, and evidence limitations.
STACKSONA / PROFESSIONAL SERVICES
Independent, evidence-based architecture and governance assessments for teams building, deploying, or scaling AI agents on AWS.
We review the boundaries around your agents, tools, permissions, approvals, and operational controls. You get a technical report your engineering team can act on, with implementation choices and a prioritized roadmap.
Defined scope Two 60-minute calls Written report No mandatory software purchase
 Architecture & control reviewEXAMPLE WORKFLOW
update_customer_recordRequest, identity, contexthuman_review = requiredScope, authorization, failure moderequest → decision → actionCorrelated audit recordUnderstand the architectureSee dependencies, access, and side effects.
Find governance gapsIdentify control questions worth resolving.
Compare the optionsAWS-native, custom, and third-party paths.
Plan the next stepsTurn findings into an engineering roadmap.
WHAT YOU RECEIVE
The deliverable is designed to be useful beyond our calls. Engineering and security teams can take the findings, review the evidence and tradeoffs, and plan work independently.
Documented system boundaries, representative agent workflows, integration touchpoints, and evidence limitations.
Security, authorization, governance, auditability, and reliability observations grounded in provided material.
Compare appropriate AWS-native, custom, and third-party approaches with the ownership and integration tradeoffs.
Prioritized improvement opportunities with concrete control outcomes and validation questions.
SEE THE DELIVERABLE
Review a nine-page, fictional example showing architecture mapping, evidence-based findings, alternatives, and a practical roadmap. The example is illustrative and is not a customer assessment.
HOW THE ENGAGEMENT WORKS
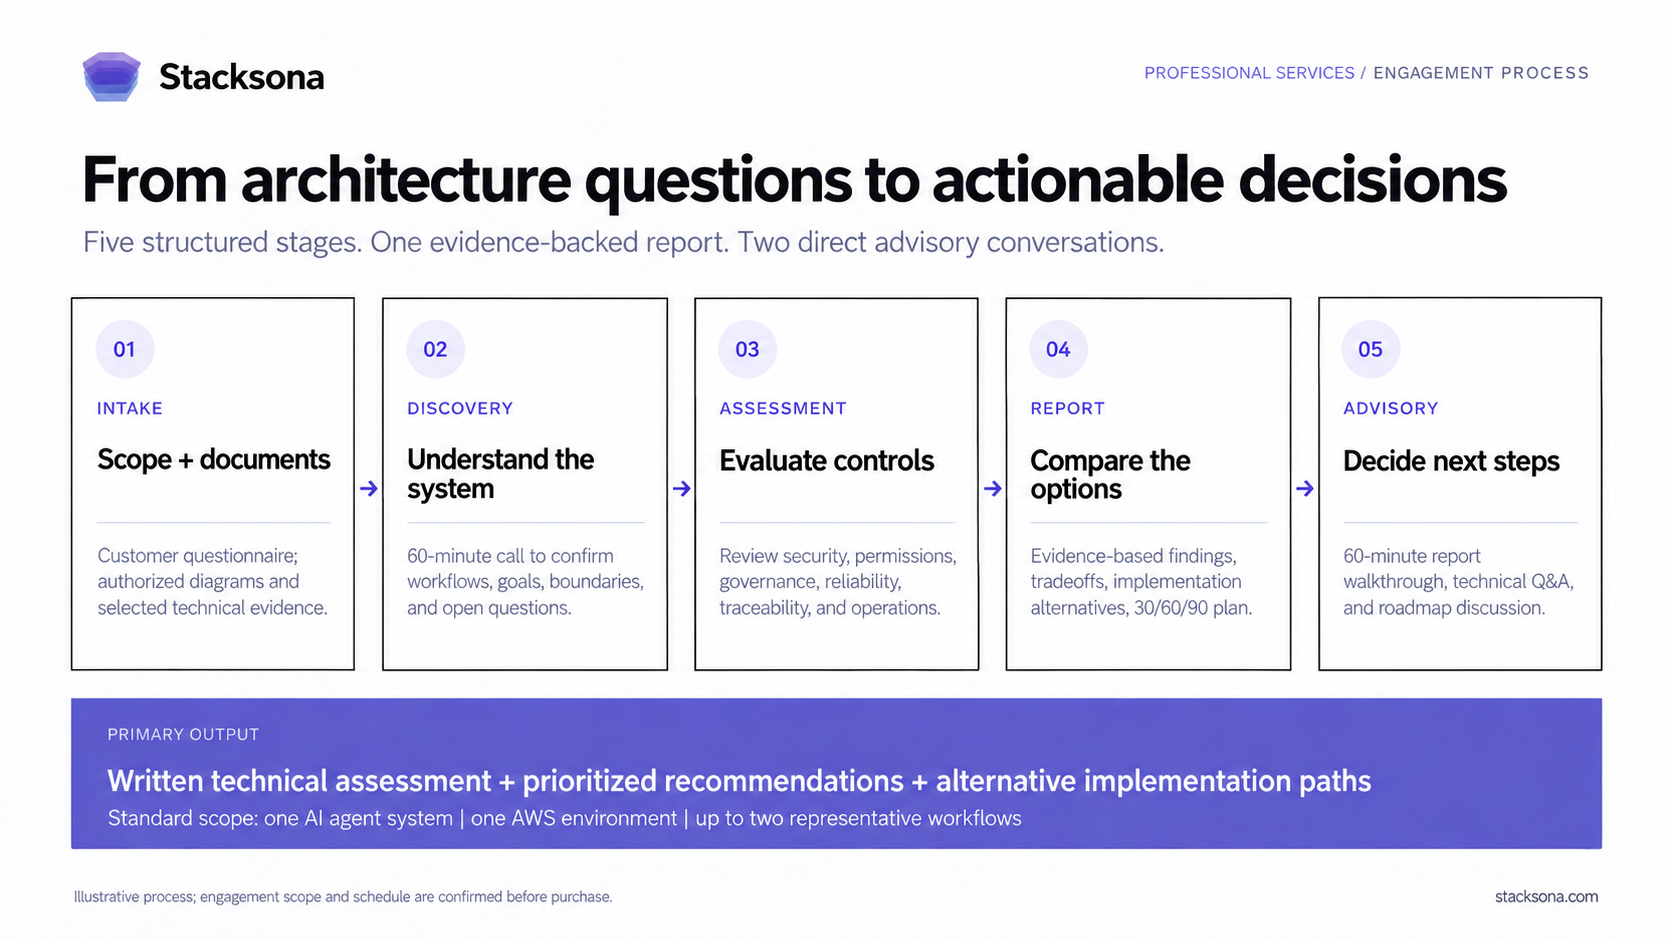
We start by understanding your system and finish by walking your team through the report and the options available for implementation.
We agree scope and collect an intake questionnaire, diagrams, and authorized technical evidence.
A 60-minute call to understand agent behavior, boundaries, goals, and unresolved questions.
Evidence-based review of architecture, permissions, governance, operational controls, and tradeoffs.
Findings, evidence limits, alternatives, and a prioritized 30/60/90-day roadmap.
A second 60-minute conversation to discuss the findings and decide practical next steps.
ASSESSMENT FRAMEWORK
The review focuses on the controls that shape what AI agents can do, how they behave when conditions change, and what evidence remains afterward.
Trust boundaries, sensitive data, agent-to-tool access, and consequential operations.
IAM, action scope, shared credentials, and read/write separation.
Approval requirements, policy ownership, exceptions, and decision checkpoints.
Timeouts, retries, idempotency, partial failures, and uncertain outcomes.
Correlation from request through decision, execution, and outcome.
Ownership, maintenance, deployments, dependencies, and observability.
Load patterns, rate limits, queues, and cost exposure.
Delegation, interface contracts, approval propagation, and control across handoffs.
SCOPE & EXPECTATIONS
The standard service is a defined technical advisory engagement. Larger systems and additional workflows are agreed separately.
Please do not send passwords, access tokens, or unredacted sensitive data. Evidence sharing and handling arrangements are confirmed before the engagement. Pricing and delivery schedule are agreed for the scope through an AWS Marketplace private offer or direct engagement.
PURCHASE AN ASSESSMENT
Select your cloud provider to contact Stacksona through its professional services listing. Pricing, delivery schedule, and final assessment scope are confirmed through an agreed offer.
Open our AWS Marketplace listing to contact Stacksona and arrange a scoped assessment through a private offer.
Purchase through AWS MarketplaceMORE CLOUD PROVIDERS
As additional cloud marketplace listings become available, this section will link directly to each provider. The assessment process and its evidence-based deliverables remain the same.
ADDITIONAL RESOURCES
Each downloadable resource is available as a standalone PDF suitable for sharing with your technical and procurement teams.
Scope, value, service boundaries, and the key deliverables in one page.
Download PDF ↗PDF / SAMPLE DELIVERABLEA fictional nine-page example of the report and practical recommendations.
Download PDF ↗PDF / PROCESSSee how the intake, discovery, review, report, and advisory call fit together.
Download PDF ↗PDF / METHODOLOGYReview the eight technical areas and the evidence-based reporting approach.
Download PDF ↗OPTIONAL IMPLEMENTATION PATH
The assessment is independently valuable. When appropriate, we compare AWS-native services, custom engineering, and governance platforms. Stacksona develops Stacksona Gate, which may be discussed as an optional implementation approach. No software license is required to purchase the assessment.
COMMON QUESTIONS
No. The technical assessment does not require a Stacksona Gate license. The report can include AWS-native, custom, and third-party options.
The standard assessment starts from architecture documentation, discovery, and selected customer-provided evidence. Any additional access must be specifically authorized and included in the agreed scope.
Yes. The written report includes actionable recommendations and alternative approaches designed to support internal planning and implementation.
Pricing is negotiated based on the agreed scope, including through AWS Marketplace private offers. There is no required software purchase.
No. The standard service is an evidence-based technical assessment. It is not a penetration test, comprehensive code audit, certification, or assurance of all components.
TAKE THE NEXT STEP
Tell us what your agents do, which AWS services are involved, and which decisions you want confidence making. Contact us through the AWS Marketplace listing to confirm fit and agree on assessment scope before any purchase.